

DomainKeys Identified Mail (DKIM) is an email authentication protocol that allows domain owners and organizations to send authenticated, digitally signed emails. This verification is made possible through cryptographic authentication.
DKIM allows receiving mail servers to verify that an email’s content hasn’t been modified during transit. In other words, it helps confirm that the message arriving in the recipient’s inbox is the same message that left the sender’s server. But what does that actually mean?
Imagine you’re at the post office sending a letter. In a basic system, no one asks for your passport or any form of identification, so anyone could send a letter while pretending to be you. This is similar to how email works with Simple Mail Transfer Protocol (SMTP). Cybercriminals can take advantage of this by sending emails that appear to come from a legitimate domain simply by entering a trusted name in the “From” field and a recipient’s address in the “To” field.
Now, imagine that the post office places a special seal on your letter to confirm that it was handled securely and wasn’t altered during delivery. DKIM works in a similar way. It adds a digital signature to an email, allowing receiving servers to verify that the message was sent by an authorized source and that its contents weren’t tampered with along the way. This helps reduce the risk of phishing attacks and other forms of email fraud.
Key Takeaways on What DKIM is in Email
- DKIM uses cryptographic authentication: Verifies that an email hasn’t been altered while traveling between mail servers.
- DKIM acts like a tamper-evident seal: Adds a digital signature that helps preserve email integrity.
- DKIM alone doesn’t stop domain impersonation: Because it doesn’t require alignment with the visible From: address, attackers can still spoof domains unless DMARC is implemented.
- DKIM is one part of a larger email security strategy: It works alongside SPF and DMARC to strengthen email authentication and reduce phishing and spoofing attacks.
What is DKIM
DKIM is an email authentication protocol that uses cryptography to verify that an email was sent by an authorized source and wasn’t modified during delivery. It helps the receiving mail servers determine whether an email can be trusted.
The protocol was developed to address one of email’s biggest security challenges: message forgery. Because the underlying email system wasn’t designed with strong identity verification, attackers can manipulate messages and impersonate legitimate senders.
By adding a digital signature to outgoing emails, DKIM creates a way for receiving servers to verify message integrity. This makes it more difficult for cybercriminals to alter emails in transit or distribute fraudulent messages that appear to come from trusted organizations.
Today, DKIM in cybersecurity is considered one of the three core email authentication standards, alongside SPF and DMARC.
How Does DKIM Work?
DKIM authentication takes place behind the scenes and relies on digital signatures, DNS records, and public key cryptography to verify message integrity. Understanding how does DKIM work becomes much easier when the process is broken down into the following simple steps:
Step 1: The Sending Server Creates a DKIM Signature
When an email is sent, the sending mail server uses a private key to generate a unique DKIM signature. The signature is created using specific parts of the message, including selected email headers and the message body. It is then added to the email header before the message leaves the server.
Because the signature is tied to the original content, even minor modifications made after the email is sent can invalidate it.
Step 2: The Domain Publishes a Public Key in DNS
For DKIM authentication to work, the sending domain must publish a public key in DNS through a DKIM record. This record allows receiving mail servers to verify signed messages without accessing the sender’s private key.
Step 3: The Receiving Server Retrieves the Public Key
When a DKIM-signed email arrives, the receiving mail server examines the message header to identify the sending domain and the DKIM selector associated with the email. Using this information, the server performs a DNS lookup to retrieve the corresponding public key.
Step 4: The Receiving Server Verifies the DKIM Signature
After retrieving the public key, the receiving server compares it with the digital signature attached to the email. The verification process determines whether the email was signed by an authorized server and whether the protected content remained unchanged during transmission.
Because only the public key is shared through DNS, the sender’s private key remains protected throughout the authentication process.
Step 5: The Email Passes or Fails DKIM Authentication
If the cryptographic values match, the email passes DKIM authentication. If the verification process fails, the receiving server flags the message as potentially suspicious. The final action depends on the recipient’s email security policies and whether additional authentication protocols, such as SPF and DMARC, are in place.
The entire process takes only a few seconds and occurs automatically before the message reaches the recipient’s inbox.
What is Public-Key Cryptography?
DKIM relies on a security model known as public-key cryptography, a cryptographic method widely used to protect digital communications, online transactions, software updates, and email authentication. Unlike traditional encryption methods that rely on a single shared key, public-key cryptography uses two mathematically related keys that serve different functions. One key is used to create a digital signature, while the other is used to verify it.
Think of it as a lock-and-key system. A sender locks a message with one key, and the recipient verifies its authenticity with another. Although the two keys are connected, one can’t be used to recreate the other. In the case of DKIM, the key used to generate the signature remains private and is never exposed outside the sending environment. The verification key, on the other hand, is published in DNS so that receiving mail servers can access it when validating incoming messages.
This approach allows organizations to verify email integrity without sharing sensitive cryptographic information. As a result, receiving servers can confirm that an email came from an authorized source and that its content wasn’t altered during transmission.
The Two Keys of DKIM: Public and Private
DKIM authentication depends on two separate keys that work together to create and verify digital signatures. Although these keys are mathematically related, they perform completely different functions.
The separation between signing and verification is what makes DKIM both practical and secure. One key remains under the sender’s control, while the other is made publicly available through DNS.
Private Key
The private key is stored securely on the sending mail server and is responsible for generating the DKIM signature that’s attached to outgoing emails. Every time an email is sent, the mail server uses this key to create a unique signature based on selected portions of the message, including specific header fields and the message body.
Because the private key controls email signing, it should never be publicly accessible. If an attacker gains access to it, they could generate valid signatures and send authenticated emails while impersonating the domain. For this reason, organizations should protect private keys carefully and rotate them periodically as part of their email security strategy.
Public Key
The public key is published in DNS through a DKIM record and is available to any receiving mail server that needs to verify a signed email.
When a message arrives, the recipient’s server retrieves the public key and compares it with the digital signature included in the email header. If the values match, the message passes DKIM authentication. Unlike the private key, the public key is designed to be shared. Making it publicly accessible doesn’t create a security risk because it can only be used for verification, not for generating signatures.
Separating these two keys adds an important layer of protection. Even if someone can view the public key, they can’t use it to create legitimate signatures or send authenticated messages on behalf of the domain.
What is a DKIM Record?
A DKIM record is a modified TXT record that’s published in your domain’s DNS. The record contains the public key that receiving mail servers use to verify the DKIM signature attached to your outgoing emails. This verification process helps confirm that the message was sent by an authorized server and that its contents weren’t modified during transmission.
Unlike SPF, which validates the sending server’s IP address, DKIM focuses on message integrity. The receiving server retrieves the public key from DNS, compares it with the signature embedded in the email header, and determines whether the message passes authentication.
A DKIM record is also linked to a selector, which acts as an identifier that tells receiving servers which public key should be used for verification. This allows organizations to maintain multiple DKIM keys for different email services, business units, or third-party email providers.
What Does a DKIM Record Look Like?
A typical DKIM record contains several tag-value pairs that define how receiving mail servers should validate signed messages. The most important elements include:
- v=DKIM1: Specifies the DKIM version.
- k=rsa: Identifies the cryptographic algorithm used to generate the key pair.
- p=: Contains the public key that’s used to verify the email signature.
A DKIM record usually follows this format:
selector._domainkey.example.com IN TXT “v=DKIM1; k=rsa; p=MIGfMA0GCSqGSIb3DQEBAQUAA4…”
Because public keys can be several hundred characters long, DKIM records often appear much longer than standard DNS records. Creating them manually can increase the likelihood of formatting errors, which is why many organizations rely on tools such as the EasyDMARC DKIM Record Generator to simplify the process.
What is a DKIM Header?
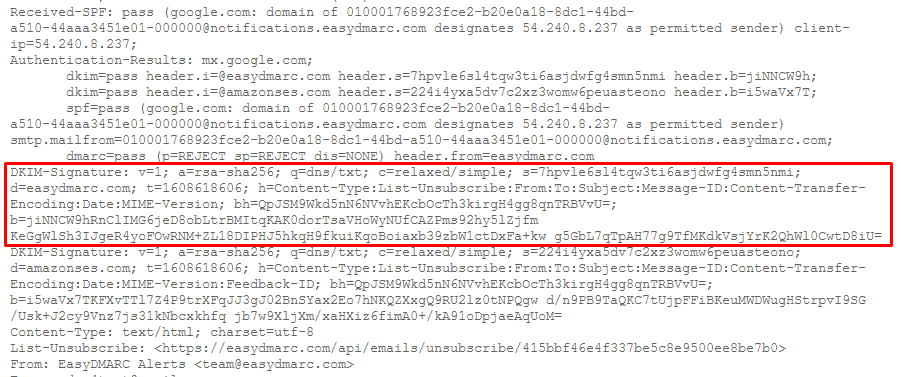
A DKIM header is a section of an email that contains the information required to validate a DKIM-signed message. It’s automatically added by the sending mail server and is typically invisible to everyday email users unless they view the message source. The header stores several parameters that guide the verification process. These include the signing domain (d=), the DKIM selector (s=), the cryptographic algorithm used to create the signature (a=), the list of signed headers (h=), and the digital signature itself (b=).
Receiving mail servers use this information to locate the correct public key in DNS and verify the message. If any of the protected fields have been modified after the email was signed, the verification process fails.
Analyzing DKIM headers is also an important troubleshooting technique. Email administrators often inspect them to diagnose authentication failures, identify misconfigured email services, and verify whether messages are being signed correctly.
What is a DKIM Signature?
A DKIM signature is an encrypted code added to email headers that serves as a digital seal of authenticity. Once you’ve enabled DKIM signing for your email service (like in Google Workspace, Office 365, or OpenDKIM with Postfix), your email server automatically performs the following steps:
- It calculates the hash value of the mail body
- It encrypts this hash using your private key
- It attaches the hash as a signature in the email header before sending
This automated process, known as DKIM signing, creates a verifiable seal that recipient servers can check against your published public key. The signature itself is essentially the encrypted hash of your email, locked with your private key that only your domain possesses.
When receiving servers process incoming email, they use this signature to verify both the sender’s identity and message integrity, forming a key component of your overall DMARC protection strategy.
Here is an example of a DKIM signature:
What is a DKIM Selector?
A DKIM selector is a unique identifier in a DKIM-signed email that tells receiving mail servers which public key to retrieve from DNS. Instead of storing all public keys in a single DNS record, DKIM uses selectors to organize and distinguish between multiple keys. This allows a domain to maintain separate keys for different email providers, applications, or business functions.
For example, an organization might use one selector for Microsoft 365, another for a marketing platform, and a third for transactional emails. If one key needs to be replaced or rotated, administrators can update that specific selector without affecting other email services.
Selectors are published as part of a DKIM record and appear in the email header as the s= tag. A receiving server combines the selector with the signing domain to locate the correct DNS record and complete the authentication process.
DKIM vs. SPF vs. DMARC: What’s the Difference?
SPF, DKIM, and DMARC are often discussed together because they’re the three pillars of modern email authentication. However, they solve different problems and shouldn’t be viewed as competing protocols.
SPF verifies the sending server. DKIM verifies the message itself. DMARC brings these technologies together and tells receiving servers how to handle authentication failures.
Implementing only one protocol leaves gaps in your email security strategy. Organizations should deploy all three to improve email deliverability, reduce spoofing attempts, and strengthen protection against phishing attacks.
| Protocol | Primary Function | What it Verifies |
| SPF | Validates the sending server | Was this email sent from an authorized IP address? |
| DKIM | Validates message integrity | Was this email modified after it was sent? |
| DMARC | Enforces authentication policies | What should happen if SPF or DKIM fails? |
SPF: Verifies the Sending Server
Sender Policy Framework (SPF) authenticates emails by verifying whether the sending server is authorized to send messages on behalf of a domain. Domain owners publish a list of approved IP addresses in DNS. When an email arrives, the receiving server checks whether the sending IP address appears in that list.
While SPF helps prevent unauthorized servers from sending emails, it doesn’t verify whether the message content has been modified during transit.
DKIM: Verifies the Integrity of the Message
DomainKeys Identified Mail (DKIM) uses digital signatures to verify that an email hasn’t been altered after it was sent. Instead of focusing on the sending server, DKIM focuses on the message itself. A receiving server validates the email by comparing the DKIM signature in the email header with the public key published in the domain’s DNS record. This additional verification layer helps protect against message tampering and strengthens trust in email communications.
DMARC: Connects SPF and DKIM
Domain-based Message Authentication, Reporting, and Conformance (DMARC) builds on SPF and DKIM by introducing domain alignment and policy enforcement. If an email fails authentication, DMARC tells receiving servers whether the message should be delivered, quarantined, or rejected. It also provides reporting that helps domain owners identify unauthorized email activity.
Without DMARC, attackers may still be able to impersonate a domain even when SPF and DKIM are configured.
To learn more about how these three protocols work together, read our detailed guide on SPF vs. DKIM vs. DMARC.
Benefits of DKIM
Implementing DKIM does more than add a digital signature to your emails. It strengthens email security, improves sender reputation, and supports better email delivery.
While DKIM isn’t a standalone solution against spoofing, it provides several operational and security benefits when deployed correctly.
Protects Email Integrity
One of the biggest advantages of DKIM is its ability to protect message integrity. Email messages often pass through multiple servers before reaching the recipient. During this process, unauthorized modifications can occur intentionally or accidentally. DKIM helps receiving mail servers detect these changes by comparing the email’s digital signature with the public key stored in DNS. If the protected content doesn’t match the original signature, the message fails authentication.
This verification mechanism helps organizations ensure that business-critical communications, such as invoices, password reset emails, account notifications, and customer updates, reach recipients in their original form.
Improves Email Deliverability
Mailbox providers such as Gmail, Microsoft, and Yahoo increasingly rely on authentication signals when deciding whether an email should be delivered to the inbox, filtered into spam, or rejected.
A properly configured DKIM implementation demonstrates that a domain follows recognized email authentication standards. This increases trust between sending and receiving mail servers and contributes to a stronger sending reputation over time.
For organizations that rely on email for marketing, sales, customer support, or transactional messaging, better deliverability directly affects engagement and campaign performance.
Supports DMARC Enforcement
DMARC doesn’t replace DKIM. Instead, it uses DKIM authentication results to determine whether a message aligns with the domain displayed in the From address. Without DKIM, organizations reduce the number of authentication signals available to DMARC, limiting its effectiveness.
Implementing DKIM creates a stronger foundation for DMARC enforcement, making it easier to move from a monitoring policy to stricter quarantine and reject policies. This is particularly important for organizations working toward full email authentication compliance.
Simplifies Email Authentication Across Multiple Services
Modern organizations rarely send all email from a single platform. Marketing campaigns, customer support systems, CRM platforms, help desk applications, and internal communication tools often use different email providers. DKIM allows each service to sign emails using its own key and selector while maintaining authentication under the same domain.
This flexibility makes it easier to manage email authentication across multiple platforms without disrupting existing workflows.
Limitations of DKIM
Although DKIM is an important email authentication protocol, it isn’t a complete solution for protecting domains against spoofing and phishing attacks. Like any security technology, it has limitations that organizations should understand before relying on it as their primary defense mechanism.
Recognizing these limitations is essential because many of them are addressed by complementary protocols such as SPF and DMARC.
DKIM Doesn’t Verify the Visible Sender Address
One of the biggest limitations of DKIM is that it doesn’t authenticate the domain displayed in the From field that recipients see in their inboxes.
A message can technically pass DKIM authentication even if the signing domain and the visible sender address belong to different domains. This creates an opportunity for attackers to exploit legitimate DKIM signatures while still impersonating a trusted brand. This limitation is one of the main reasons DMARC was introduced. DMARC requires domain alignment, ensuring that authentication results are associated with the same domain presented to the recipient.
Email Modifications Can Break DKIM Authentication
DKIM signatures are generated using specific parts of an email, including selected headers and portions of the message body. If an email is modified after it’s signed, the authentication check can fail. Some mailing lists, forwarding services, and security gateways automatically alter messages by adding disclaimers, reformatting content, or modifying headers.
Although DKIM implementations can be configured to tolerate certain changes, extensive modifications may still invalidate the signature. This can create authentication challenges in complex email environments that involve multiple intermediaries.
DKIM Doesn’t Prevent Compromised Accounts
DKIM verifies that an email was signed using an authorized domain key, but it doesn’t evaluate the intent behind the message. If an attacker gains access to a legitimate email account or compromises an authorized sending platform, they can still send malicious emails that successfully pass DKIM authentication.
In other words, DKIM validates the technical authenticity of a message, not the trustworthiness of its content. Organizations should combine email authentication with access controls, multi-factor authentication, and employee security awareness training.
DKIM Requires Ongoing Key Management
Implementing DKIM isn’t a one-time configuration task. Organizations must continuously manage cryptographic keys, DNS records, email providers, and authentication policies. Keys should be rotated periodically to reduce security risks, and DNS records should be updated whenever email infrastructure changes. This becomes increasingly important for organizations that rely on multiple third-party platforms to send email.
Without regular maintenance, DKIM records can become outdated, misconfigured, or inconsistent across different services, reducing the effectiveness of email authentication.
How to Check Your DKIM Record
Configuring DKIM is only the first step. You should also verify that your DKIM record is publicly accessible and correctly configured in DNS. Even a small formatting error, an incorrect selector, or an incomplete public key can prevent receiving mail servers from validating your DKIM signature. As a result, legitimate emails may fail authentication checks and experience deliverability issues.
The easiest way to verify your configuration is to use the EasyDMARC DKIM Lookup tool. Simply enter your domain name and selector to retrieve your published DKIM record and confirm that it’s available to receiving mail servers.
A DKIM lookup can also help identify common configuration problems, including missing DKIM records, invalid selectors, incorrectly published public keys, and DNS propagation issues.
EasyDMARC Makes DKIM Easy
At EasyDMARC, we make DKIM easy. DKIM is a critical component of your email security strategy, and it cannot be overlooked. It works by adding a cryptographic signature to your emails, ensuring that they haven’t been tampered with during transit. This simple yet powerful process helps prevent issues such as email spoofing, phishing, and other malicious attacks that can damage your reputation and harm your recipients.
With EasyDMARC, you can easily generate your DKIM record using our intuitive DKIM record creator. You can also verify your DKIM setup using our DNS record checker to ensure the record is correctly published and accessible. Our set of tools guides you through the setup process, helping you avoid common errors and ensuring your DKIM configuration is correct. By implementing DKIM, you’ll significantly reduce the chances of your domain being exploited for phishing attacks or other fraudulent activities.
Don’t let your email server run unprotected. Get started with EasyDMARC’s 14-day free trial and safeguard your email communications.
Frequently Asked Questions
Technically, you can send emails without DKIM; however, doing so may increase the risk of your emails being marked as spam or rejected by recipients’ servers. Implementing DKIM enhances your email’s credibility and deliverability.
Yes, in most cases, DKIM is more important than SPF when it comes to DMARC. This is because SPF alignment cannot always be achieved with certain ESPs, and auto-forwarding can easily break SPF, while DKIM remains intact. Additionally, DKIM provides other benefits, such as helping build your domain’s reputation, enabling data visibility in Google Postmaster, and supporting other Feedback Loop (FBL) services.
SPF verifies that emails come from authorized mail servers, helping to prevent unauthorized senders from spoofing your Return-Path domain.
DKIM, on the other hand, uses cryptographic signatures to confirm that the email content hasn’t been altered in transit. Because a DKIM signature remains intact even after forwarding, it is generally more reliable for email authentication and domain reputation building.
Together, SPF and DKIM play a crucial role in email authentication, and both work toward full DMARC compliance.
To set up DKIM:
1. Generate DKIM Keys: Use a DKIM key generator to create a public-private key pair
2. Add Public Key to DNS: Publish the public key as a TXT record in your domain’s DNS settings
3. Configure Your Email Server: Set up your email server to sign outgoing emails with the private key
If you use a third-party email provider like Google Workspace, HubSpot, or other ESPs, the provider handles the private key storage and gives you the public key. You simply need to copy and paste it into your DNS records.
For a simpler setup, EasyDMARC has identified over 1,500 email sources and provides all the necessary details for DKIM configuration.

 We’re glad you joined EasyDMARC newsletter! Get ready for valuable email security knowledge every week.
 You’re already subscribed to EasyDMARC newsletter. Continue learning more about email security with us


