
A DMARC fail is when an email sent from a domain fails to pass authentication checks, leading to potential rejection or quarantining. Understanding why DMARC fails is essential to safeguarding your domain from phishing and spoofing threats and ensuring high email deliverability rates. DMARC authentication, an email security protocol, works with SPF (Sender Policy Framework) and DKIM (DomainKeys Identified Mail) to verify the legitimacy of emails sent from your domain.
Key Takeaways
- DMARC fails when neither SPF nor DKIM passes and aligns with the domain in the visible From header.
- Only one of the two has to pass and align. SPF passing on its own is not enough if the domain does not match.
- The four most common causes are DKIM signed with the provider’s domain, third-party senders that were never authorized, forwarding, and spoofing.
- What happens to a failing message depends on your policy: p=none delivers it, p=quarantine sends it to spam, p=reject blocks it at the receiving server.
- DMARC aggregate reports identify which sending source is failing and whether the problem is SPF, DKIM, or alignment.
What does a DMARC Failure Mean?
DMARC failure occurs when an email sent from your domain does not pass the DMARC check. DMARC passes when at least one of SPF or DKIM authenticates the message, and the domain it authenticated aligns with the domain in the visible “From” header. A failure means neither condition was met.
In practical terms, the DMARC fail meaning is straightforward: neither SPF nor DKIM produced a valid, aligned result for the domain in the visible From address.
Domain alignment, the core concept of DMARC, compares the domain in the From header against the domains validated during authentication. This alignment requires that the domain in the SPF check (based on the Envelope From or Return-Path address) or the DKIM signing domain (represented as d=example.net) match the domain shown in the “From” address.
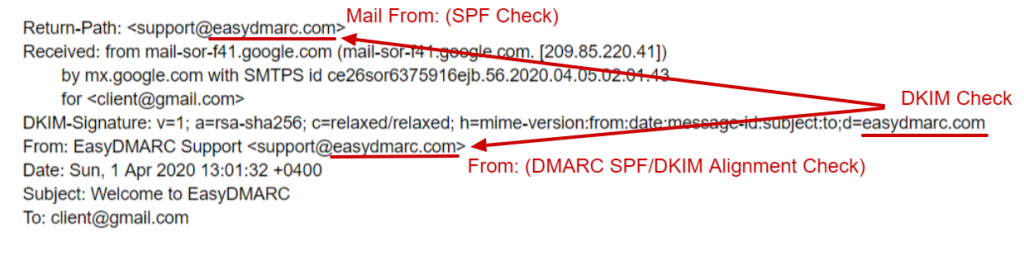
When neither SPF nor DKIM produces an aligned result for the “From” domain, DMARC fails, indicating that the email could be unauthorized or fraudulent. Proper SPF and DKIM alignment is essential to secure your domain and reduce the risk of misuse.
What Happens When DMARC Fails?
What happens to a failing message is determined by the policy published in your DMARC record, not by DMARC itself. The receiving server reads the policy and acts on it.
- p=none: the message is delivered normally, and the failure is recorded in your aggregate reports.
- p=quarantine: the receiving server is asked to treat the message as suspicious, which usually means the spam folder.
- p=reject: the receiving server is asked to refuse the message outright, and the sender receives a bounce.
Across a domain, repeated failures produce:
- Emails landing in spam folders instead of inboxes
- Complete rejection of messages by receiving mail servers
- Delivery delays affecting time-sensitive communications
- Damage to your domain’s sending reputation
- Potential security alerts for your recipients
When you encounter a DMARC error, it signals that something in your email authentication chain isn’t working properly. This authentication problem can significantly impact your email deliverability and business communications.
Common Causes of DMARC Failure
Most DMARC failures trace back to one of four conditions. The first two are configuration gaps on your side, the third is a limitation of how forwarding works, and the fourth means someone else is using your domain.
1. DKIM Signature Not Set Up
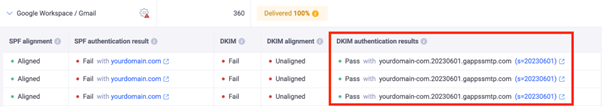
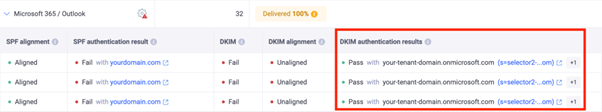
If you don’t configure a custom DKIM signature, email providers like Google and Microsoft will automatically sign your outgoing emails with their default DKIM key (e.g., d=domain.gappssmtp.com for Google). These default signatures don’t represent your domain; instead, they reflect the email provider’s domain. To set up DKIM under your domain, you need to configure the correct DKIM entries in your DNS provider such as GoDaddy, Rackspace, or Cloudflare.
In this case, DMARC fails because of email domain misalignment. If someone receives an email from example.com but it’s signed as example.gappssmtp.com or example.onmicrosoft.com, DMARC won’t recognize it as authorized. You can view examples of this issue, along with screenshots, in the EasyDMARC dashboard.
A DMARC fail due to Google Workspace using the default DKIM Signature, and not authorized in the SPF Record
A DMARC fail due to Microsoft 365 using the default DKIM Signature, and not authorized in the SPF Record
Here’s how you can set up SPF, DKIM, and DMARC for Google Workspace and Microsoft 365 mail.
2. Third-Party Senders Were Never Authorized on Your Domain
If you use third-party service providers like MailChimp, SendGrid, HubSpot, and ZenDesk for your marketing, transactional, and help desk emails, you have to permit them to send emails on your domain’s behalf.
That is achieved by pointing DNS entries from your DNS Provider (like GoDaddy, Cloudflare, or Rackspace) to authorize and ‘whitelist’ the given servers.
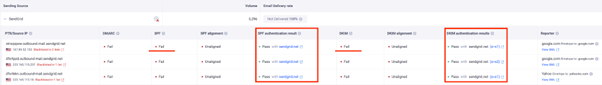
These providers sign your emails with their domain name by default, and your recipients generally see “via sendgrid.net”, “via thirdpartyprovider.com” messages on your emails, thus leading to DMARC misalignment and DMARC failure.
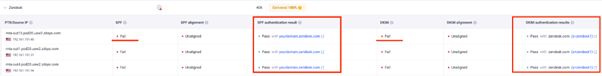
Below you can see examples of this case, with screenshots from the EasyDMARC dashboard.
A DMARC fail due to emails sent through a SendGrid account not properly signed with DKIM and SPF for a unique domain.
A DMARC fail due to emails sent through a ZenDesk account not properly signed with DKIM and SPF for a unique domain.
3. Email Forwarding Has Changed the Original Message
Forwarded emails can often trigger DMARC failures due to the way they are processed by intermediary servers. When an email is forwarded, it may pass through one or more intermediate servers before reaching its final destination. These intermediary servers often have IP addresses that differ from the original sender’s, which can lead to SPF check failures, as the new IP addresses aren’t typically included in the original sender’s SPF record. Although DKIM is generally unaffected by forwarding, modifications by intermediary servers, such as adding or changing message footers, can sometimes disrupt the DKIM signature.
4. Your Domain Has Been Spoofed
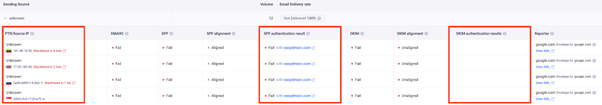
If you are a victim of spoofing, cybercriminals are sending emails that appear to come from your domain. Why does DMARC fail in this case? These unauthorized sources don’t pass SPF and DKIM authentication checks, which results in DMARC failure. These failed attempts are categorized under the ‘Threat/Unknown’ tab in your EasyDMARC Dashboard.
How to Identify Why DMARC Is Failing
Before changing any DNS record, establish which check failed and for which sending source. Fixing SPF when the problem is DKIM alignment wastes a reporting cycle, so knowing how to fix DMARC failure errors starts with identifying the exact cause.
Read the Authentication-Results Header
Open a failing message and view the original headers. If your DNS authentication results show “DMARC fail,” start by comparing the authenticated domains against the visible From address. The Authentication-Results line records the outcome of each check, including the SPF result and the domain it evaluated, the DKIM result and the d= domain that signed it, and the DMARC result. Comparing those two domains against the From address usually identifies the failure on its own. An email header analyzer parses the header if you would rather not read it raw.
Check Your Aggregate Reports
Aggregate reports cover every source sending under your domain, including ones you may not know about. They show pass and fail counts per source along with the SPF and DKIM results behind each one. The DMARC XML report analyzer converts the raw XML into a readable per-source view.
Reporting is aggregate and covers a reporting window, typically a day, so a source that started failing today appears once the next report arrives.
Separate Authentication Failures From Alignment Failures
Both produce a DMARC fail, and they need different fixes.
- Authentication failed: SPF returned a fail or permanent error, or the DKIM signature did not verify. The record or the key is the problem.
- Authentication passed but did not align: SPF or DKIM passed on the provider’s domain instead of yours. The record is valid, and the domain is wrong.
The second is the more common of the two, and it is the reason a source can look correctly configured while still failing DMARC. How closely the domains have to match depends on whether your record uses strict or relaxed DMARC alignment.
How to Fix DMARC Failures
If you’re trying to understand how to fix DMARC failure issues, most cases come down to one of these six areas, and they’re worth working through in order.
Ensure SPF Alignment
- Check that your SPF record includes all legitimate sending sources for your domain. If you’re using third-party email services (like marketing platforms or web hosts), ensure their sending IP addresses are included in your SPF record.
- Ensure that the Envelope From or Return-Path address used during email delivery matches your domain or the domains you’ve authorized in your SPF record.
- Confirm your SPF record stays within the 10 DNS lookup limit. Exceeding it returns a permanent error that DMARC evaluates as an SPF failure, even though the record looks valid, which is usually resolved by flattening or consolidating includes.
To better understand how domain alignment affects authentication results, learn more about SPF alignment and its role in improving DMARC compliance.
Configure DKIM Properly
- Set up a DKIM digital signature for your domain to sign outgoing emails. If you use third-party email services, ensure they sign emails with your domain’s DKIM key (not their default).
- Check that the d= value in the DKIM signature matches your domain.
- You can use a DKIM record checker to confirm the key published for a selector resolves correctly.
Check Your Domain Alignment
- For DMARC to pass, the domain in the From email header must match the domain used in the SPF and DKIM alignment checks. If you’re using an email service provider or forwarding service, ensure their systems support proper alignment and don’t modify the message in a way that causes misalignment.
Review Your DMARC Policy
- Ensure your DMARC policy is correctly configured in your DNS settings with a free DMARC checker. You can also start with a p=none policy for monitoring over the first few weeks. Focus on detecting legitimate sources and authenticating them using SPF and DKIM best practices, and then gradually shift to p=quarantine or p=reject as you resolve issues. Closely examine your DMARC reports to identify misalignments or authentication failures.
If you’re troubleshooting authentication failures, it’s also important to test your domain for DMARC readiness by checking SPF and DKIM configuration, domain alignment, and legitimate sending sources before moving toward stricter enforcement.
Monitor Your DMARC Reports
- Use DMARC aggregate reports and forensic or failure reports to track which emails are failing DMARC checks. These reports will help you identify which IPs or services are causing SPF or DKIM issues.
- DMARC reports arrive as XML. The platform parses them, and the dashboard displays each sending source categorized as Compliant, Non-Compliant, Threat/Unknown, or Forwarded, so you can separate a misconfigured legitimate sender from an unauthorized one without reading the raw files.
Consult with Your Email Service Providers
- If third-party services are involved, work with them to ensure proper configuration of your SPF, DKIM, and DMARC records.
You can find more about DMARC in our blog on the DMARC RFC.
How to Verify the Fix Worked
Publishing a corrected record is not the same as confirming it works. Verification runs in three steps, and each one tells you something the previous step can’t.
Confirm the Record Is Published
Check that the corrected record resolves before testing mail. Resolvers keep serving the previous value until its TTL expires, so allow the full TTL to elapse before treating a lookup result as final. A DMARC check and an SPF record checker confirm what is live.
Send a Test Message and Read the Headers
Send through the source you fixed and inspect the Authentication-Results header on the received message. This is the fastest confirmation available, because it reflects a real evaluation by a receiving server rather than the contents of a DNS record.
Confirm Across a Full Reporting Cycle
A single test message confirms one path. Aggregate reports confirm the source as a whole. Watch the source across the next reporting cycle and check that its pass rate rises and stays there, since some failures only appear on a subset of traffic such as forwarded mail or a second sending IP.
How to Prevent DMARC Failures Long-Term
Most DMARC failures are introduced by a change somewhere else: a new marketing tool, a rotated DKIM key, a DNS edit made without reference to the authentication records.
- Authorize new senders before they send. Configure SPF and DKIM on your domain as part of onboarding any new service, rather than after the first failure appears in a report.
- Keep an inventory of sending sources. Aggregate reports surface every source using your domain, which is the practical way to maintain that list across departments.
- Monitor continuously instead of auditing periodically. The platform monitors authentication status across all your domains, and alerts notify you when a source changes status.
- Watch SPF lookup count as you add services. Each new include brings the record closer to the 10 lookup limit. EasySPF keeps the record within the limit as sources change.
- Move to enforcement in stages. Start at p=none, resolve the failures visible in reports, then move to p=quarantine and p=reject once every legitimate source is authenticating.
In Closing
Understanding DMARC failures is part of protecting your domain from phishing and spoofing attacks. Proper SPF and DKIM configuration, along with domain alignment, are essential to pass DMARC checks. Common causes of failure include misconfigured DKIM signatures, third-party service misalignments, email forwarding issues, and domain spoofing. By aligning your domain correctly, monitoring DMARC reports, and ensuring proper configuration, you can minimize these failures and enhance your email security. The EasyDMARC platform monitors SPF, DKIM, and DMARC across all your domains, and reports show which sending sources are failing and why, so failures surface before they affect delivery.
Frequently Asked Questions
A DMARC failure means a message sent from your domain did not satisfy the DMARC check. DMARC passes when at least one of SPF or DKIM authenticates the message, and the domain it authenticated matches the domain in the visible From header. If neither condition is met, the message fails, and your published policy determines what the receiving server does with it.
Send a message to an address you control and open the original headers. The Authentication-Results line shows the SPF result, the DKIM result with the signing domain, and the DMARC outcome. For a view across all your sending sources rather than one message, check your aggregate reports.
Identify which check failed first. If SPF failed, confirm the sending IP is authorized, and the record stays within the 10 DNS lookup limit. If DKIM failed, confirm the selector is published, and the d= domain is yours rather than your provider’s. If both passed but DMARC still failed, the problem is alignment, and the fix is configuring the sending service to authenticate on your domain.
DMARC aggregate reports contain per-source SPF and DKIM results, but they arrive as XML that is impractical to read directly. Report analyzers parse that data into a per-source view. In EasyDMARC, the dashboard displays each sending source with its SPF and DKIM results and categorizes it as Compliant, Non-Compliant, Threat/Unknown, or Forwarded.
Recurring failures from the same source usually mean that source was never authenticated on your domain, so it keeps signing with the provider’s domain and failing alignment. Recurring failures across many sources point to an SPF record that has exceeded the lookup limit or a DMARC record published at the wrong host. Failures that appear and disappear are often forwarding, which breaks SPF by design.
Aggregate reporting arrives on a reporting cycle, so alerting is built on changes in reported status across that cycle. Configure alerts on the conditions that matter, such as a source dropping below its usual pass rate or a new unrecognized source appearing.
Yes. Under p=none, DMARC takes no action on the message, though the receiver’s other filters may still apply, and the failure is only recorded in your reports. Under p=quarantine and p=reject, the receiving server is asked to filter or refuse it, though the final decision rests with the receiver.
No. One aligned pass is enough. A message where SPF fails but DKIM passes and aligns with the From domain will pass DMARC. Configuring both is still worth doing, because DKIM survives forwarding and SPF usually does not.
The DNS change takes effect as soon as the previous TTL expires, commonly within an hour. Confirming the fix takes longer, since aggregate reports are typically sent daily. Expect a full reporting cycle before a source shows a clean result.
 We’re glad you joined EasyDMARC newsletter! Get ready for valuable email security knowledge every week.
 You’re already subscribed to EasyDMARC newsletter. Continue learning more about email security with us